About the book
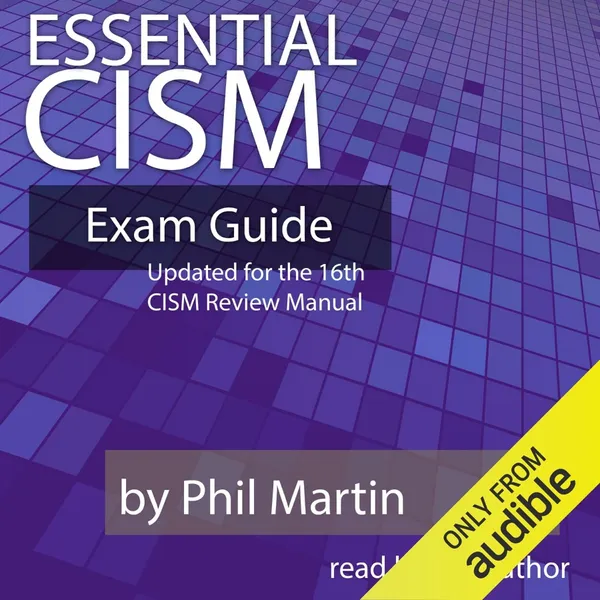
Essential CISM has been written with a single goal in mind - to present the CISM material in a way that is easy to absorb without leaving any content behind. Plenty of examples are included to drive the points home so that when it comes time to take the CISM exam, you are ready! This exam guide covers all four ISACA domains, including: Information security governance Information risk management Information security program development and management Information security incident management The book is broken down into two sections. Section 1 covers basic concepts you will need to understand before hitting each domain. The CISM official exam guide is overwhelmingly redundant across the domains, and so in this book you will encounter each topic once instead of having to rehash the same subject in different (and chaotic) ways. By the time you start covering the domains, you will already be 60 percent of the way there! Section 2 presents the four domains and ties together the concepts covered in Section 1, plus subjects that are unique to each domain. Please note that chapters may not have a descriptive name as displayed on your mobile device - this is limitation of the publisher platform. However, each chapter will always start with the title being read aloud, so it should be fairly simple to scan through chapters when you wish to revisit a subject.
Highlights that stuck
The principle of least privilege is an approach that segments all resources so that we can increase access as-needed. This allows us to give people access only to the bare minimum resources they need to do their job. The downside of this approach is that it requires a well-thought-out plan from the very beginning and requires increased attention to ensure resources are properly segmented.
Need-to-know is a security approach that requires a person to not only have the proper authority to access resources, but also a valid need to do so. For example, it is not enough to be given authority to read customer files – your role in the company must also require it. This provides an extra layer of security to keep information out of the wrong hands.
Segregation of duties, or SOD, is a security mechanism that prevents a single role from having too much power. For example, in a bank, the same person who prints a check should not have the ability to change the name on that check – it should require a different person to execute both actions. This greatly reduces the chance of fraud.
Criticality is the impact that the loss of an asset will have, or how important the asset is to the business. For example, if the loss of a specific IT system would prevent orders from being processed until the system is returned to a usable state, it is most definitely critical to the business. On the other hand, payroll processing is not as critical – while the permanent loss of the ability to pay employees would certainly cause a mass exodus of people at some point, we can probably absorb a lengthier downtime.
Sensitivity is the impact that unauthorized disclosure of the asset will have, meaning that people that should not see information are able to get to it. Consider a scenario in which we want to keep the recipe to our secret sauce from getting out. The leakage of this information would not impact our day-to-day operations, so it is not considered to be critical. But, we would be losing one of our core advantages over competitors, and so the recipe is said to have a high sensitivity.
Assurance, related to security information, means that we can manage security risks by keeping vulnerabilities and threats to a level that we can live with. For example, if we deploy a firewall and encryption techniques to help protect access to a database, then we are assuring the database is being kept secure.
The total cost of ownership, or TCO, represents the true cost to own an asset, as opposed to just the cost to initially acquire it. TCO at a minimum covers the original cost, any upgrades, ongoing maintenance, support, and training.
governance is the act of creating a plan on how a company will achieve a goal and then making sure everyone executes that plan.
Governance is the responsibility of the board and company executives. These folks at the top might delegate a lot of the footwork, but they are ultimately responsible to ensure the plan is properly implemented.
A strategy doesn’t have to tell us how we’re going to carry out each step, or how long it will take, or the problems we might face along the way. It just lays out a road map of how we are going to reach our goal.
119 highlights in my Readwise library; these are the ones I keep coming back to.